About Nexora
Security testing and compliance consultation, built on hands-on delivery experience.
The Next Generation Trust
"At Nexora, we believe the next generation of cybersecurity is not just about finding vulnerabilities — it's about building resilience, trust, and compliance into every digital transformation."
Who we are
Nexora is a Hong Kong-based cybersecurity and security-consultation practice with delivery capability extending into India. We work with organizations that need a clear, honest picture of their security posture — and practical help closing the gaps that matter, not a long list of low-value findings.
Our focus is secure digital transformation and audit-ready compliance: helping clients adopt new technology without losing control of risk, and helping them demonstrate that control to regulators, auditors, and customers.
Founder profile
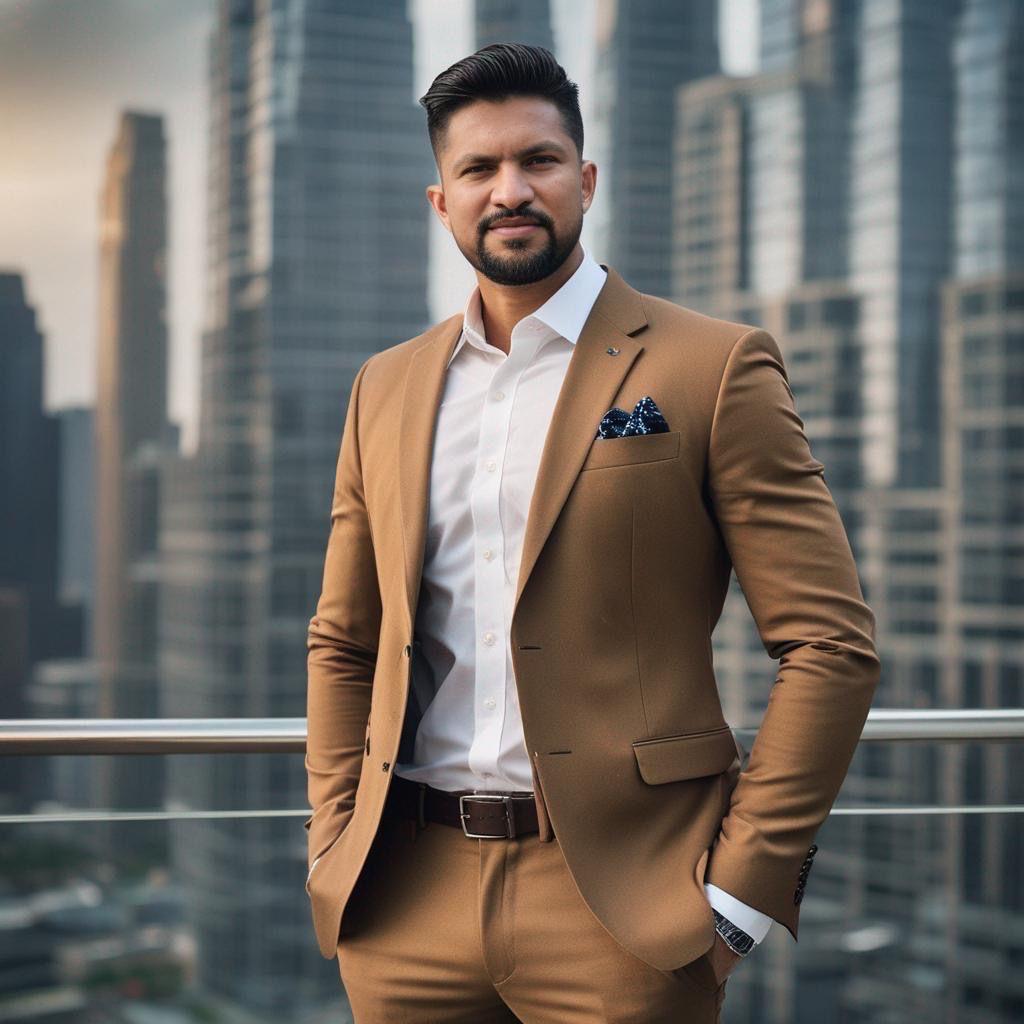
Jithin Nedumkallel Kurian
Founder & Principal Security Consultant, Nexora — Hong Kong
Nexora is led by a security practitioner with 18+ years in IT and over 15 years in information security leadership, having delivered engagements across insurance, aviation, oil & gas, banking, and healthcare clients throughout Asia-Pacific. That background spans vulnerability assessment and penetration testing, cloud security, and DevSecOps, alongside regulatory and compliance work aligned to ISO 27001/27701, PCI DSS, NIST, and GDPR — including hands-on delivery of red-team engagements using MITRE ATT&CK methodology.
Notable work includes the responsible disclosure of a stored/reflected XSS vulnerability in a production SAP system (CVE-2020-6368), building and leading regional security teams, and managing Asia-Pacific vendor and RFP programs while reporting risk posture directly to senior leadership — the same rigor that now underpins how Nexora runs every engagement.
Certifications
Why clients work with us
Independent
No product to sell you — our only interest is an accurate assessment.
Practical
Findings come with remediation guidance your team can actually act on.
Accountable
We re-test after remediation, so sign-off means the issue is actually closed.